5 Best Practices For Encryption Key Management Brilliance Safety Journal
Enterprise encryption key management techniques (KMS) are options designed to handle, store, and protect cryptographic keys across entire organizational cryptographic environments. These methods securely deal with each public and private keys, ensuring correct key technology, storage, rotation, and access control while enforcing strict safety policies. Many KMS options additionally incorporate audit logs to trace key usage, supporting regulatory compliance and risk administration. Automation performs an more and more essential position in key administration methods. Between frequent key rotation and escalating key volumes, it’s typically too difficult for IT teams to keep up with manual processes.

Encryption keys are one of the accessible forms of higher-end security measures as a result of they eliminate unauthorized entry and stop breaches. Key sprawl happens when organizations generate keys without a central stock or governance process. Untracked keys create orphaned encrypted datasets and expose decryption functionality to accounts without documented authorization. Most corporations hold their encryption keys within the cloud or store them in physical hardware security modules. If your encryption key’s managed properly, encrypted knowledge will be secure.
Options
These principles might not apply to all techniques or all forms of keys. Ephemeral keys can provide excellent forward secrecy protection, which suggests a compromise of the server’s long term signing key does not compromise the confidentiality of past periods. Symmetric key-wrapping keys are used to encrypt different keys utilizing symmetric-key algorithms. Posture administration provides a unified view of what cryptographic property exist, where they are deployed, and the way they’re configured. Cryptographic posture is essential in order to know what is underneath the hood, but in addition to be properly ready. Automation is the enabler that makes each different key management best follow sustainable at scale.
Encryption management is one software in an arsenal of risk mitigation methods that maintain keys unknown however in constant rotation. Shorter cryptoperiods scale back per-key exposure home windows however impose re-encryption costs and increase operational complexity. For high-volume databases, re-encryption on rotation requires compute assets and upkeep home windows that conflict with availability requirements. The broader regulatory and technical landscape is described within the knowledge safety supplier network function and scope reference. The follow intersects directly with the broader knowledge security suppliers that define control classes applicable to regulated industries.
- You simply need to know why it issues, and who to belief to assist you get it proper.
- Integration with SIEM instruments is helpful for combining multiple logs and for additional analysis and reporting.
- A sturdy key management answer offers you clear visibility into all cryptographic operations and provides audit logs for compliance, inner critiques, or security investigations.
- We’re here to know your business, identify your dangers, and implement solutions that really make a difference.
What’s Cloud Security? Types, Dangers & Advantages Outlined
A MAC is a cryptographic checksum on the information that is used so as to provide assurance that the data has not modified and that the MAC was computed by the expected entity. Earlier Than a company can manage its keys, it’s best practice https://sportscasualties.com/as-cybersecurity-insurance-premiums-rise-what-can-businesses-do-to-cope.html to first find them all. Coverage ought to have the right balance of confidentiality, integrity and availability, coping with the pure pressure that come up. Constructing and deploying quantum protected cryptography represents a huge problem from the scientific, technological, logistic and infrastructure factors of view.
What Is Encryption Key Management?
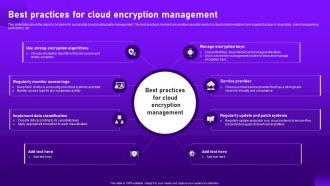
Where signing keys are concerned, Microsoft Storm-0558 key breach 2023 and Coupang Signing Key Breach are helpful examples of what happens when key retirement or offboarding fails. This is essential for compliance audits, but additionally for forensic investigations ought to a key ever turn out to be compromised. Integration with SIEM tools is beneficial for combining multiple logs and for further analysis and reporting. The distribution of keys between two or more entities involved in the communication. The process may involve a Key Technology or Key Agreement, the place a model new key is produced as a perform of the secret (key) info possessed by the individual communicating events. The first step is generating a cryptography key utilizing an permitted algorithm, including using a pseudo-random generator.
Information that has been encrypted with lost cryptographic keys won’t ever be recovered. Therefore, it is essential that the application incorporate a safe key backup functionality, especially for purposes that assist knowledge at rest encryption for long-term knowledge stores. Establish the cryptographic and key management necessities on your utility and map all parts that course of or store cryptographic key materials. Keys are a critical part of extra superior cybersecurity hygiene measures. Utilizing these best practices will safeguard encryption keys on a personal and industry stage.
Key Administration Dangers – What Risks Await?
Key vaults can improve safe storage by way of enhanced access management together with encryption at relaxation. These vaults might preserve detailed logs to disclose who accesses keys and when. With Sectigo, strict protocols forestall unauthorized individuals from recovering personal keys.